INTEGRATED SASE
INTEGRATED SASE seamlessly unifies advanced security technologies including firewalls, secure web gateway and zero trust access, into a single powerful platform that protects your data everywhere and anywhere – whether on-site or on the move.
INTEGRATED SASE will maximise your cyber defences with its 99.9% malware block rate and 100% phishing prevention from malicious URLs and zero-day threats, delivering on state-of-the-art cyber protection, compliance with evolving cybersecurity laws and regulations, and importantly, peace of mind, knowing you’re protected from the latest cyber threats.
BE secured
Unified Security
One platform protects everyone, everywhere – no gaps, no weak links
Multi-layered Security
True SASE frameworks protects against the very latest threats
World-Leading Tech
Best-in-breed technologies with 99.9% malware block rate, 100% phishing protection
Zero-Trust Confidence
Every user, device and application is checked and verified
Data Sovereignty
Purpose-built in-country gateways, data centres & cloud ensure data integrity
Resilient & Reliable
Cloud-native design delivers fast, reliable security – anywhere, everywhere, always
Simplified Management
Bulletproof your business from
cyber threats and saves time
Cost & Time Efficient
Consolidates tools & vendors, reducing staff tasks and licensing & support costs
Simple Scalability
Adapts fast as your business grows – no infrastructure headaches
Simplified Management: Centralises policy control and monitoring, reducing IT complexity and errors
Easy Scalability: Cloud-native design lets businesses quickly scale security and networking for new users, devices, and locations
Better Performance: Delivers security where it’s needed, optimising traffic for faster, more reliable access
Consistent Compliance: Enforces uniform security and compliance policies across all users and environments
Rapid Deployment: Cloud-based delivery allows for faster rollout of security and networking services across all locations
Remote Workforce Support: Provides secure, seamless access for remote and hybrid employees, regardless of where they work
Automatic Updates: Ensures the latest security features and threat intelligence are always in place without manual intervention
Unsure About the Terms SD-WAN, SASE & SSE?
Despite current myths purporting that SASE has in some way ‘replaced’ SD-WAN the facts are that an SD-WAN network & SSE security framework combined to form a SASE solution, is the ultimate secure edge network framework
OMNIA’s SASE consolidates networking and security capabilities into a unified cloud-native platform, hosted within purpose-built in-country OMNIA gateways, delivering comprehensive protection and connectivity while ensuring data sovereignty. This enables organizations to secure access to applications and data regardless of the user’s location or device.
Our Check Point Partner Status and Specialist Certifications
Why is SASE Needed For Successful Digital Transformation?
The need for SASE stems from the evolving nature of cyber threats and the changing dynamics of modern business operations. Here are several key reasons why SASE is indispensable in today’s digital landscape:
Remote Workforce: The rise of remote work has blurred the boundaries of the corporate network, making traditional security architectures obsolete. SASE enables organizations to extend security policies and enforcement to remote users, ensuring that they can access corporate resources securely from anywhere
Mobile Workforce: In an increasingly mobile world, employees expect seamless and secure access to corporate resources from their mobile devices. SASE delivers unified security policies across all endpoints, whether they are corporate-owned or BYOD (bring your own device), ensuring consistent protection against cyber threats.
Scalability and Flexibility: Traditional security appliances are often rigid and difficult to scale, especially in dynamic environments. SASE offers scalability and flexibility through cloud-native architecture, allowing organizations to adapt quickly to changing business requirements without compromising security.
Reduced Complexity and Cost: By consolidating networking and security functions into a single cloud-based platform, SASE simplifies management and reduces operational overhead. Organizations can eliminate the need for multiple point solutions, resulting in cost savings and improved efficiency
SASE Framework Components Available Within an OMNIA Solution
ZERO TRUST NETWORK ACCESS
Provides full visibility and control over users, both managed and unmanaged applications, and all devices that have access to your corporate network and services:
- Eliminate implied trust privileges
- Support 3rd party and BYOD access
- Secure access to cloud applications
An on-premise or cloud hosted security service that filters unwanted software or malware from user-initiated Internet traffic and enforces corporate and regulatory policy compliance:
- URL and content filtering
- Threat detection and threat prevention
- Data loss prevention
- SIEM, SOAR and EDR integration
An on premise or cloud-based security policy enforcement point between cloud service consumers and cloud service providers to enforce enterprise security policies when applications are accessed:
- Compliance
- Visibility
- Threat protection
- Data protection
A firewall solution delivered as a cloud-based service that allows companies to simplify IT infrastructure and supply Next Generation Firewall (NGFW) capabilities:
- Web filtering
- Advanced threat protection (ATP)
- Intrusion prevention system (IPS)
- Domain Name System (DNS) security
Why Check Point Was Chosen to Protect OMNIA Customers Globally – “You Deserve The Best Security”
Check Point is the only security vendor with a near-perfect 99.8% block rate for malware, as well as a 100% phishing and malicious URL prevention rate in Miercom’s 2024 & 2025 testing. Additional independent testing from NSS Labs in 2025 shows almost identical results, with Check Point maintaining first place.
The above success ratios were also almost identically achieved in 2023 in comparative testing by one of the world’s largest ISPs seeking an innovative SASE solution for their national infrastructure and retail environment. The OMNIA SASE solution scored an overall 98% efficacy compared with just over 70% scored by the next vendor.
Proven Security: Let Check Point and OMNIA Protect Your Business Too!
Unlike other solutions that only detect threats, Check Point prevents threats. Available as an on-premise option, running on our SD-WAN appliance, or as an ATOMIUS CLOUD SASE gateway solution, ATOMNIA and Check Point integration provides organizations of all sizes with integrated, advanced threat prevention, reducing complexity and lowering the total cost of ownership.
- Next Generation Firewall
- Advanced Threat Protection
- Secure Web Gateway
- Zero trust Network Access
- DNS Security
- Data Loss Prevention
- Email Security
- Browser Protection
- Secure SaaS Applications
- Device Posture and Compliance
- Web Application and API Protection
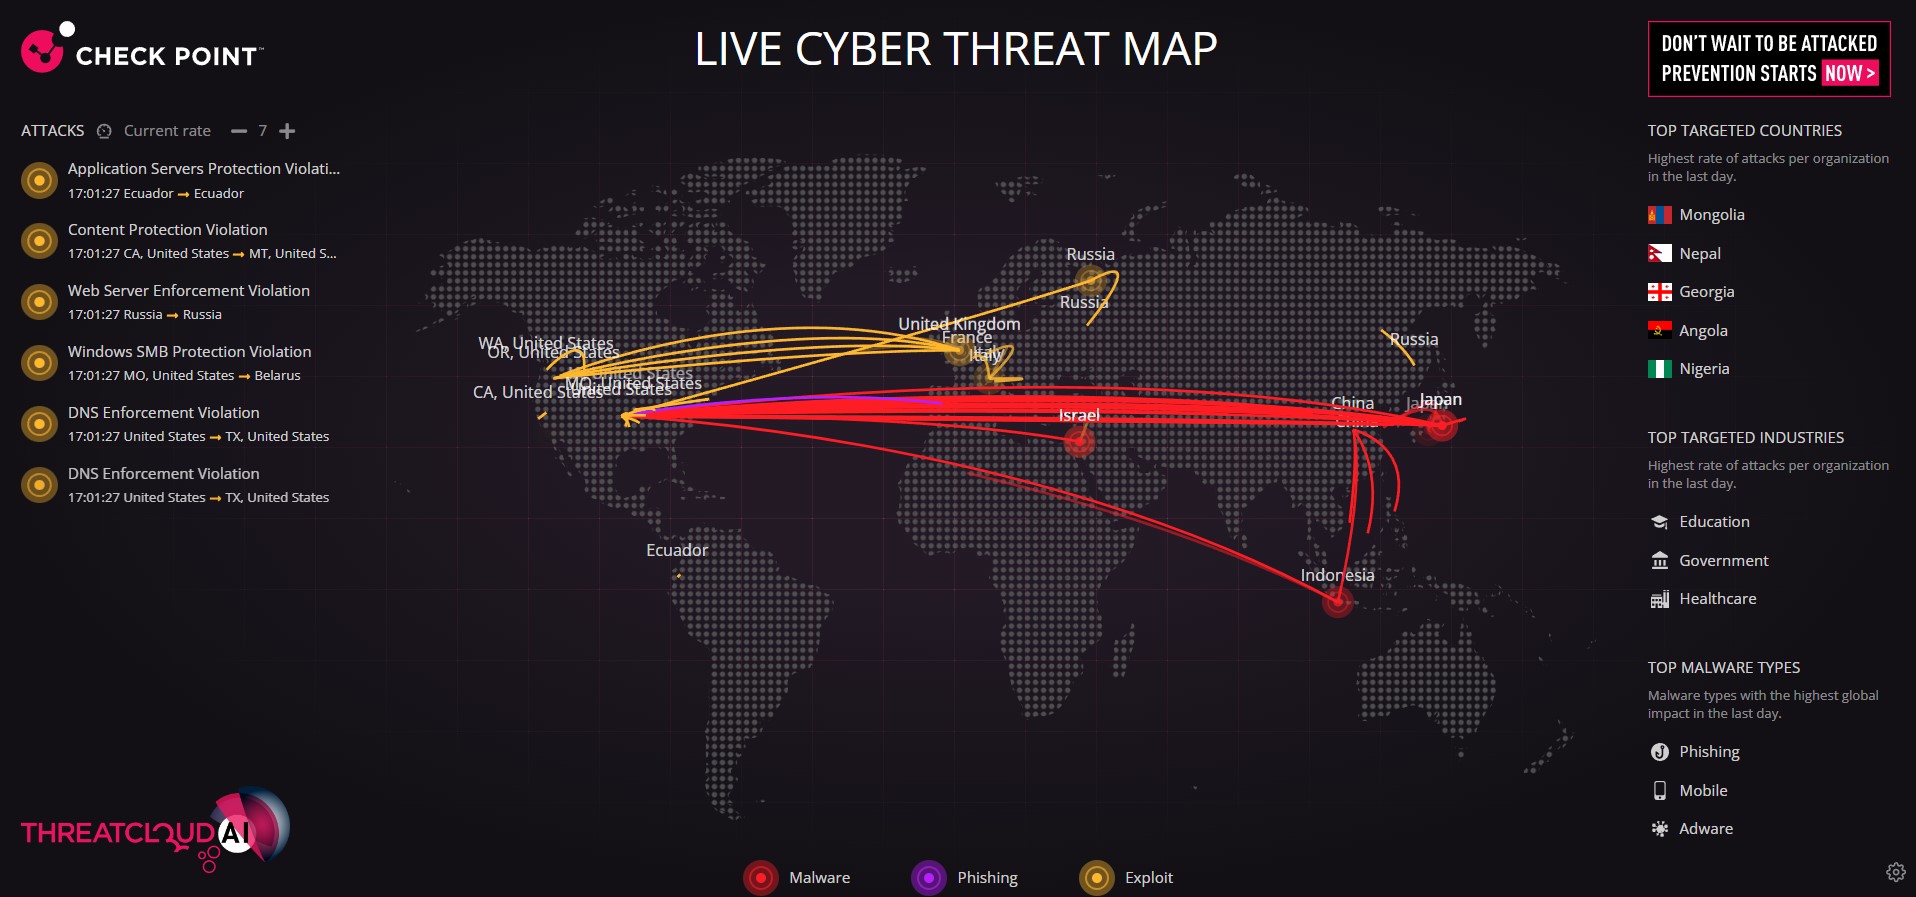
Click to view the Check Point live cyber threat map
Software Development Practices and Check Point Security Certifications
Check Point: “Information security starts at the design stage and is embedded in the lifecycle of systems, products and services. This is why Check Point follows “security by design” principles at all times at the design and architecture level, and conduct design and other reviews based on the STRIDE method. We implement a change management program regarding our products and services including maintaining development and testing environments separately from production.
We evaluate and track vulnerabilities of open source and third party libraries used in our products and services, including by performing static code analysis and manual code review where we deem required after risk analysis. Threat researchers, red teams and designated service providers carry out security verifications, such as penetration testing (PT) and multiple analysis tools”
Check Point products consistently meet and exceed the stringent requirements established by internationally recognized
standards, approval processes and independent security industry tests:
- SOC 2
- ISO / IEC 27000
- Common Criteria
- FIPS 140-2
- NSS Labs
- ICSA Labs
- Section 508
- IPv6
- NIAPC
- CSfC
- CESG NCSC CE+
Our Solutions Also Integrate Seamlessly with ZScaler, Fortinet, Netskope and Palo Alto Security Products
CONTACT US FOR MORE INFORMATION
Most SD-WAN software offers a Stateful packet firewall as standard, protecting networks and data but offering no advanced protection like Deep Packet Inspection (DPI), Intrusion Prevention System (IPS), directory based policies, Application level security and blacklisting / whitelisting. Some vendors offer a combined security and SD-WAN product, and just like SD-WAN technology, these security options differ greatly between vendors. The lines between network and security start to blur as you add in the requirement to support remote user access and access to Cloud hosted applications. These are your options:
Centralised Firewall
A centralised firewall requires all traffic to be backhauled to a central location, typically a Data centre, which is not ideal to access Cloud hosted applications and dilutes the SD-WAN benefit of being able to access applications and the Internet, directly from each location on your network.
Edge Security
A single device at every site, such as our VENA and VECTA appliances, supplies both SD-WAN and Security functionality. Both the SD-WAN and security vendor technologies can be replaced independently without changing the hardware, eliminating vendor tie-in and ensuring best of breed options for network and security.
Cloud-based Security
SD-WAN software integrates seamlessly with third party Cloud security providers, sending all necessary traffic directly to a Cloud hosted security platform, again allowing you to select best in class preferred providers in a simple, easy to manage network and security solution.
Single Vendor
Historic security vendors have bolted on SD-WAN functionality and historic SD-WAN vendors have done the same with the security function. In some cases, one funtion performs far better than the bolt-on, and users are tied to a single provider solution, often limiting potential solution benefits. Ask us which solutions to avoid, and why!
Check Your Security Right Now – With a Free CheckMe by Check Point Security Assessment
Have You got 2 Minutes to Spare – You Might Not be as Safe as You Think?
CheckMe service simulates many types of attacks that can compromise your computer and the information on your network. This service includes a series of tests that check the vulnerability of your network, endpoint, cloud and mobile to Ransomware, Phishing, Zero Day, Bot communication, Browser Exploit, anonymised usage and Data leakage.
Sample CheckMe Report
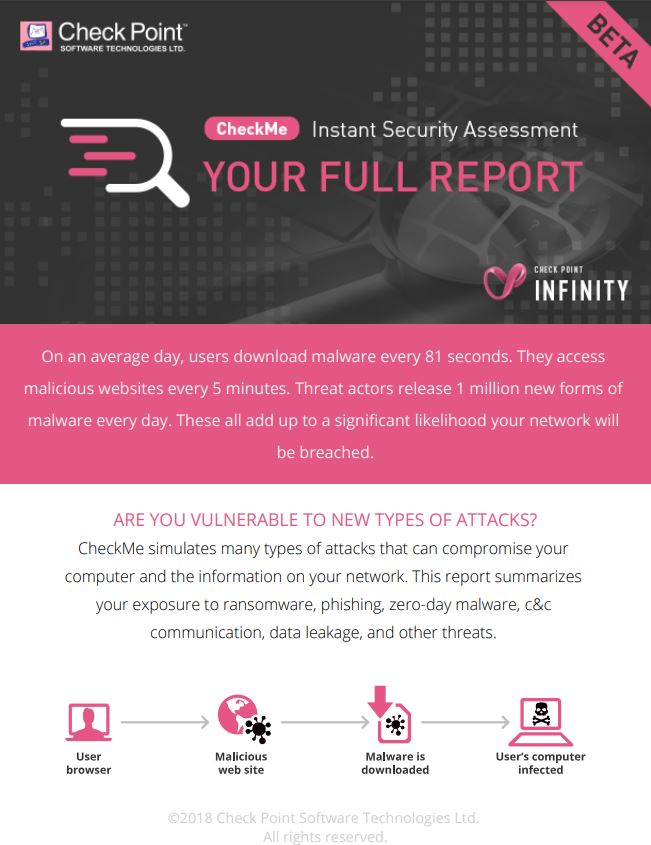
CheckMe by Check Point is a proactive assessment that identifies security risks on your network, endpoint, cloud and mobile environments. Based on this assessment, CheckMe instantly provides you with a detailed report that shows if your environments are vulnerable to:
- Ransomware is a malware that encrypts users’ files and require ransom for their decryption
- Command & Control Communication let attackers take complete control over an infected computer.
- Identity Theft attack captures personal information by fake websites that appears to be legitimate.
- Zero-day attacks use surprise to exploit holes in the software that are unknown to the vendor.
- Malware Infection lets attackers take complete control over an infected computer.
- Browser Exploit is an attack that takes advantage of a particular vulnerability in a computing system.
- Anonymous surfing can open backdoors into an organization’s network
- Data leakage unintentional or theft release of sensitive information outside the organization’s network.
- Cloud Segmentation scans for open ports of accessible machines within the same environment to indicate for access.
- Click anywhere here to be re-directed to the Check Point CheckMe website and select the environments you wish to assess (Network, Endpoint and/or Cloud).
- CheckMe runs independently and analyzes your environments.
- Your web browser communicates with CheckMe service to analyze your network’s security controls (without any actual risk for your network).